01 Investigation
An investigation with a plan and a budget
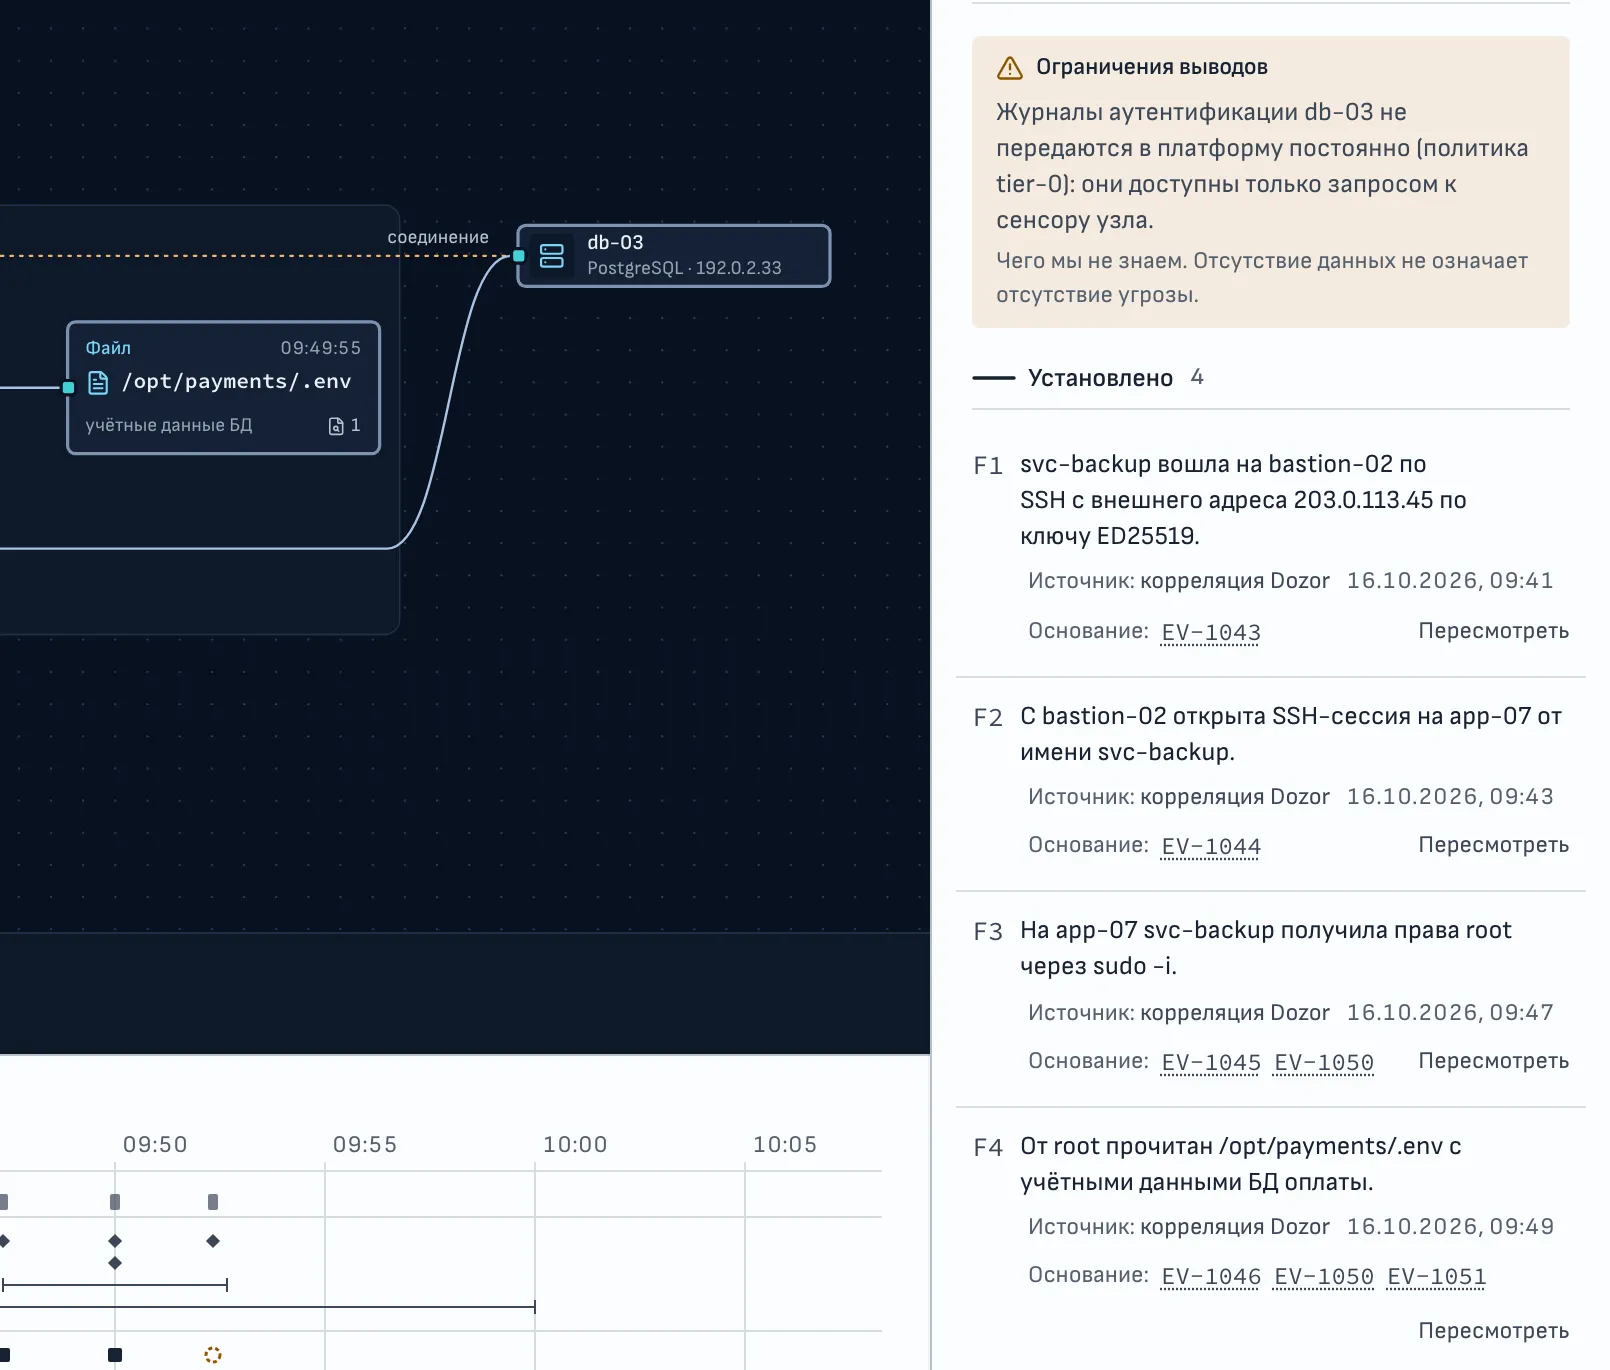
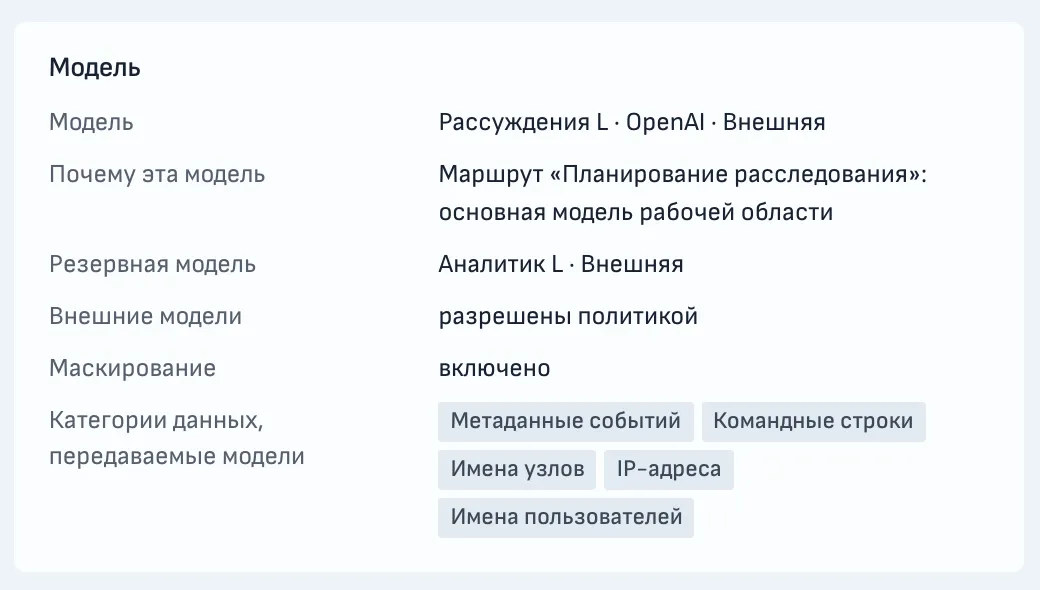
The AI investigator drafts a plan of read-only queries, collects telemetry and host data and returns a conclusion with recommendations. Every step is shown with the tokens and cost it took.
Console for the duty shift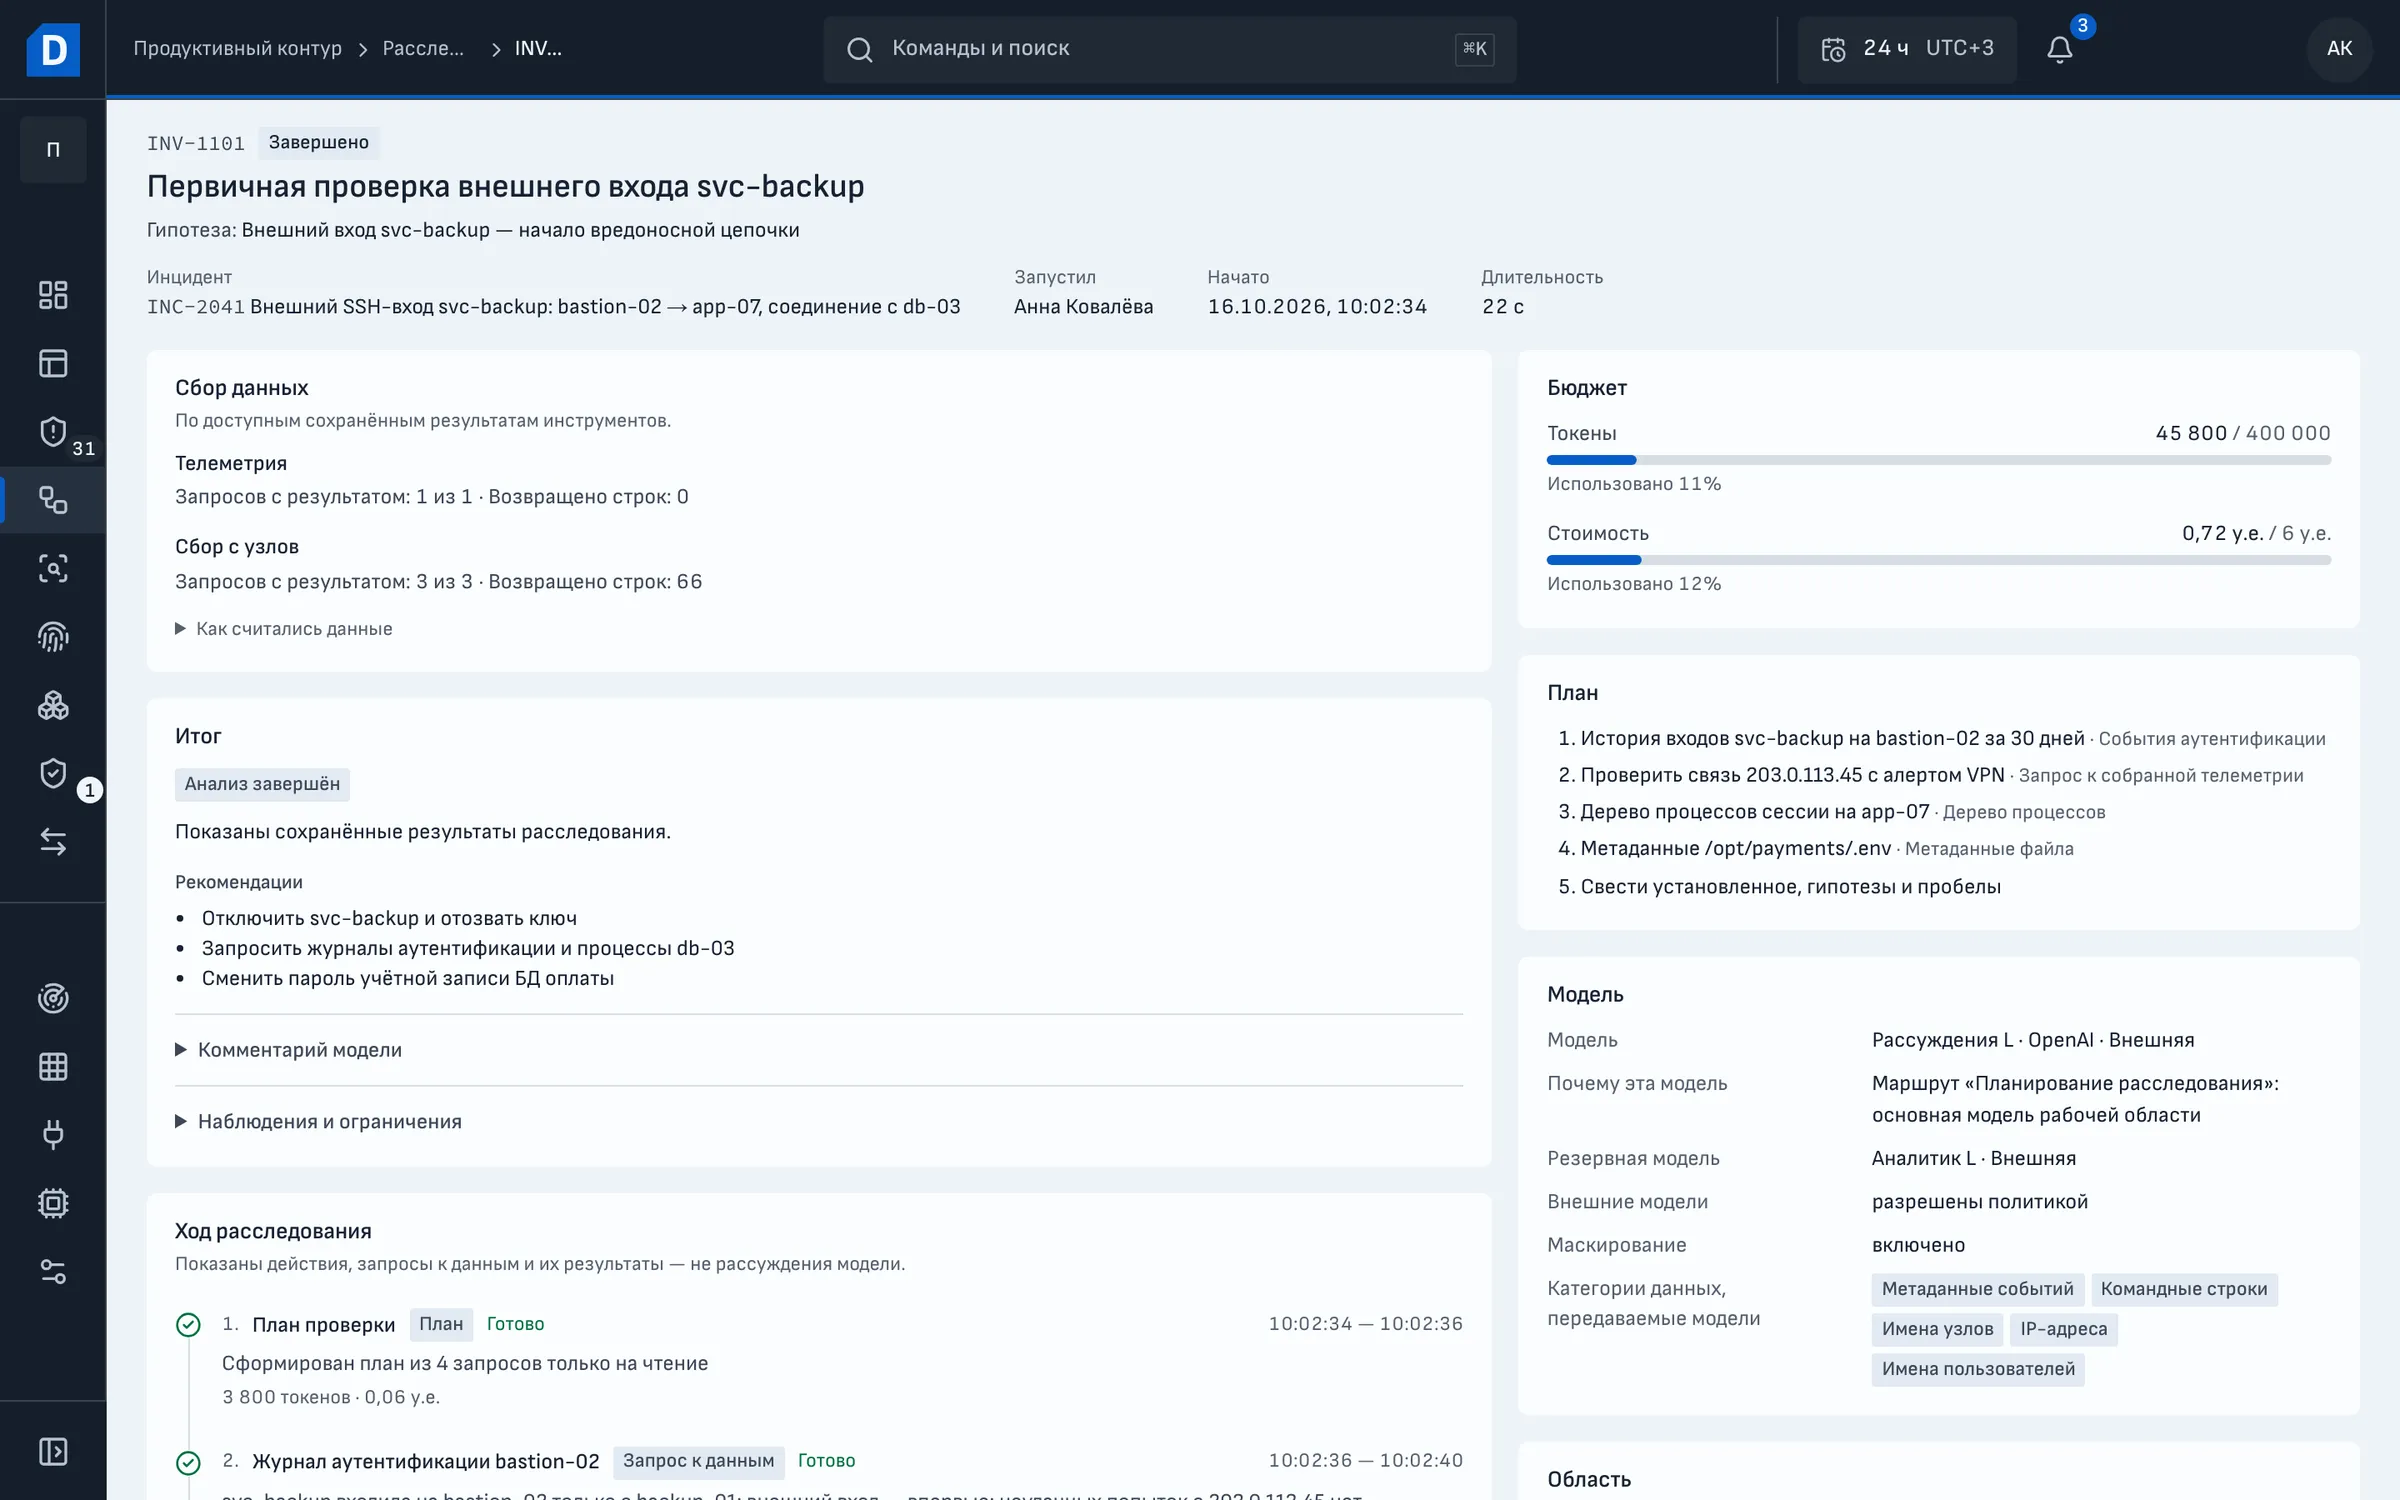
Manual alert triage
An analyst triages alerts by hand, switching between consoles and pulling data from servers until the traces are gone.
Agent for Linux, Windows and macOS
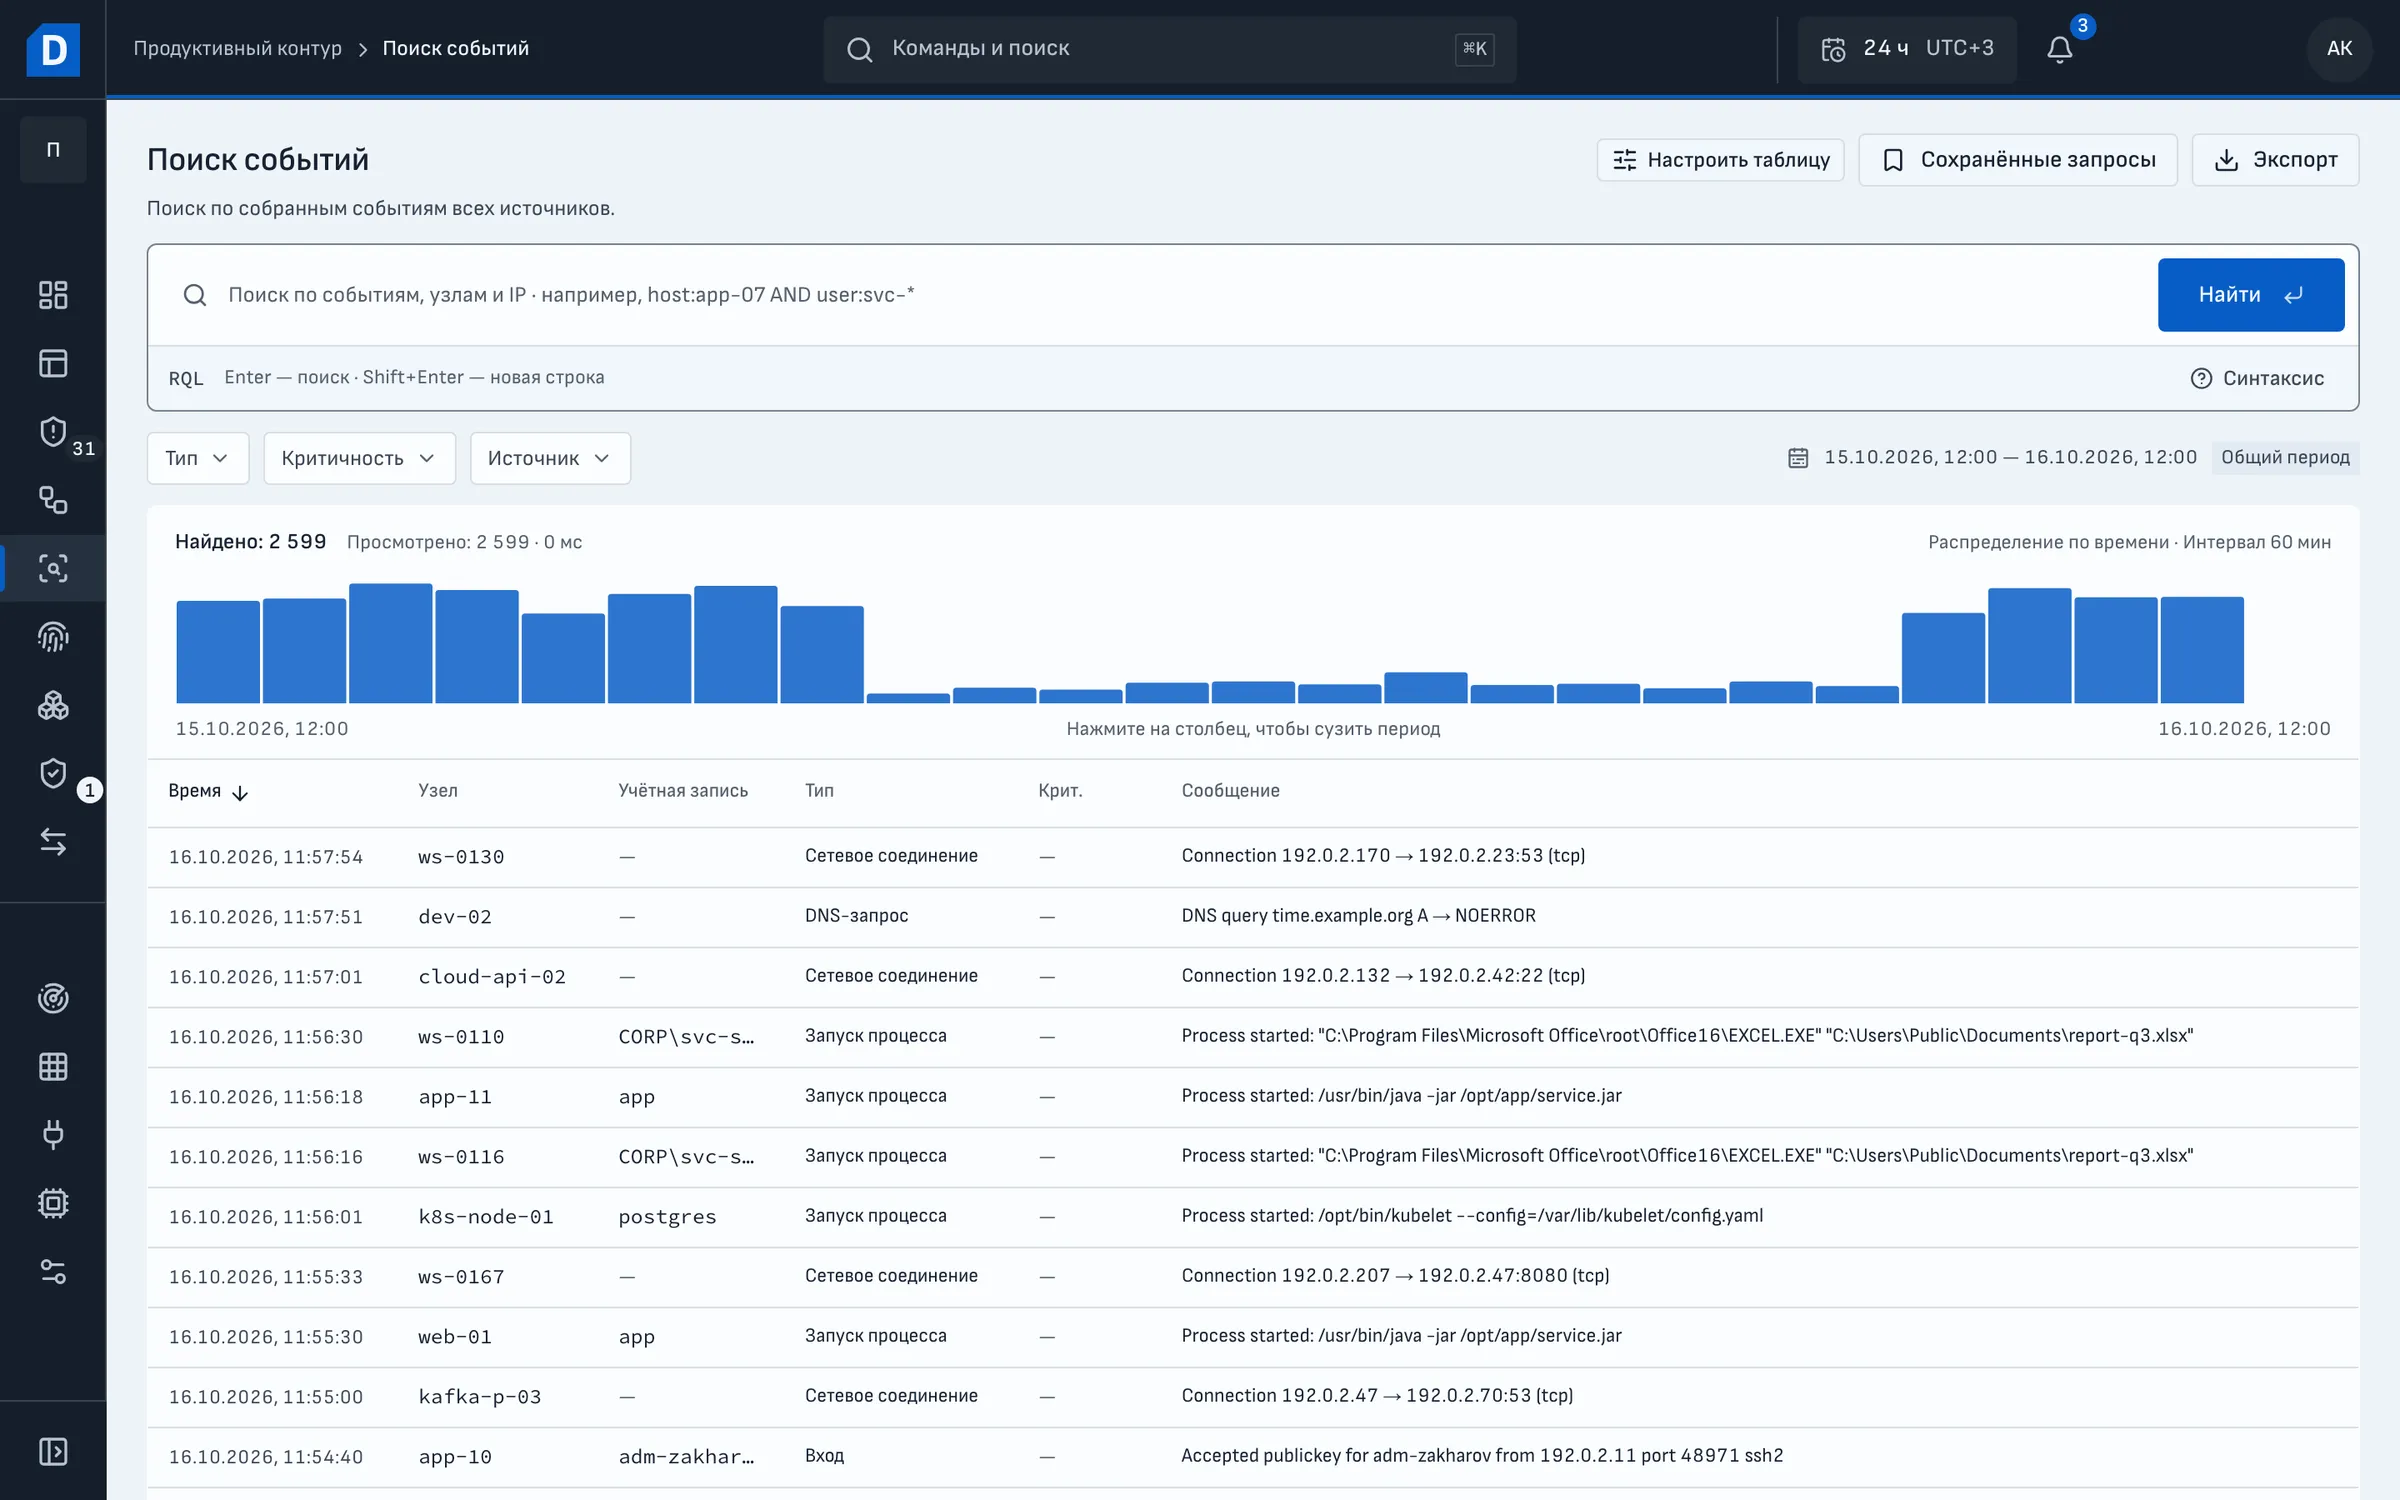
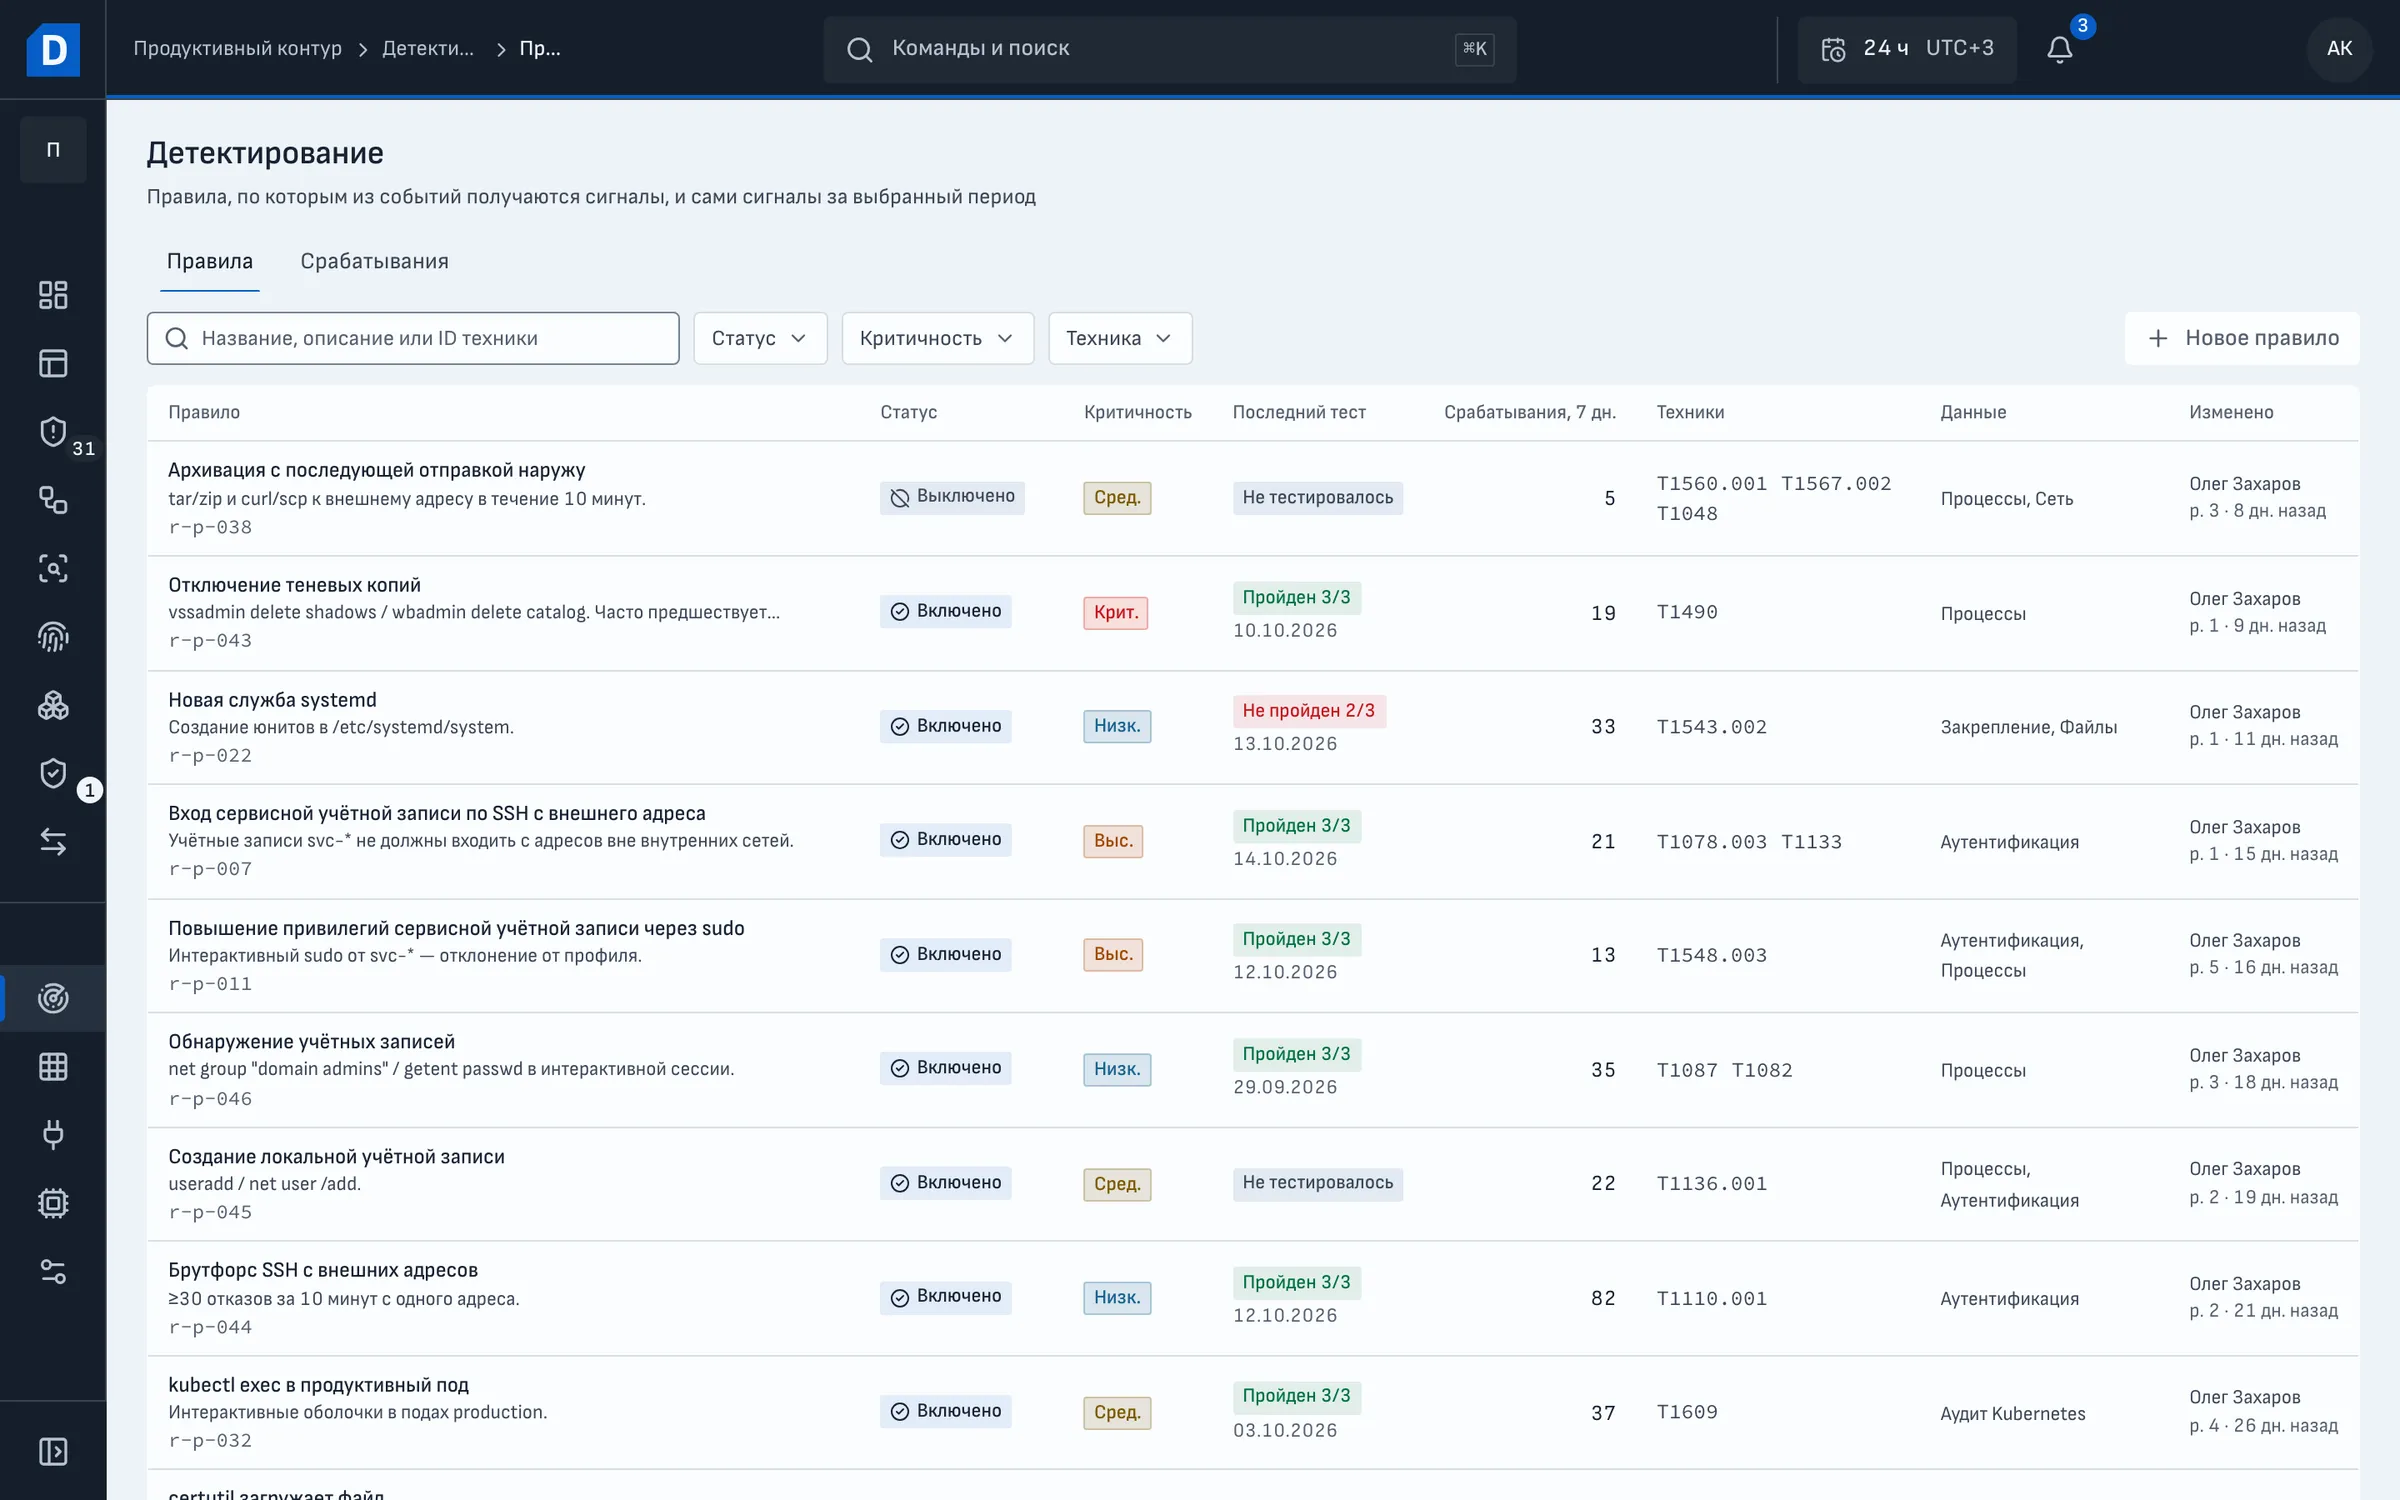
The Dozor agent records process launches, file access, network connections and privilege escalation on the server. From these records the analyst reconstructs what a user did after signing in.
The agent connects to the hub over mTLS (TLS 1.3) and opens no inbound ports. Kernel-level monitoring is read-only: agent rules record events and do not block processes. On Linux the agent uses eBPF, on Windows the event log, on macOS Endpoint Security.
Sign-ins
SSH sign-ins and sessions: who, from where and with which key.
Logs
Logs of services, web servers, containers and journald. Rotation, truncation and deletion of logs.
Processes and privileges
The process tree, sudo and escalation to root, including attempts the kernel denied.
Files
Reads of secrets and writes to cron, systemd, authorized_keys and PAM.
Kernel
Loading of modules and BPF programs, debugging of other processes.
Network
Inbound and outbound connections tied to a process.
app-07, Dozor agent 1.24
read-only
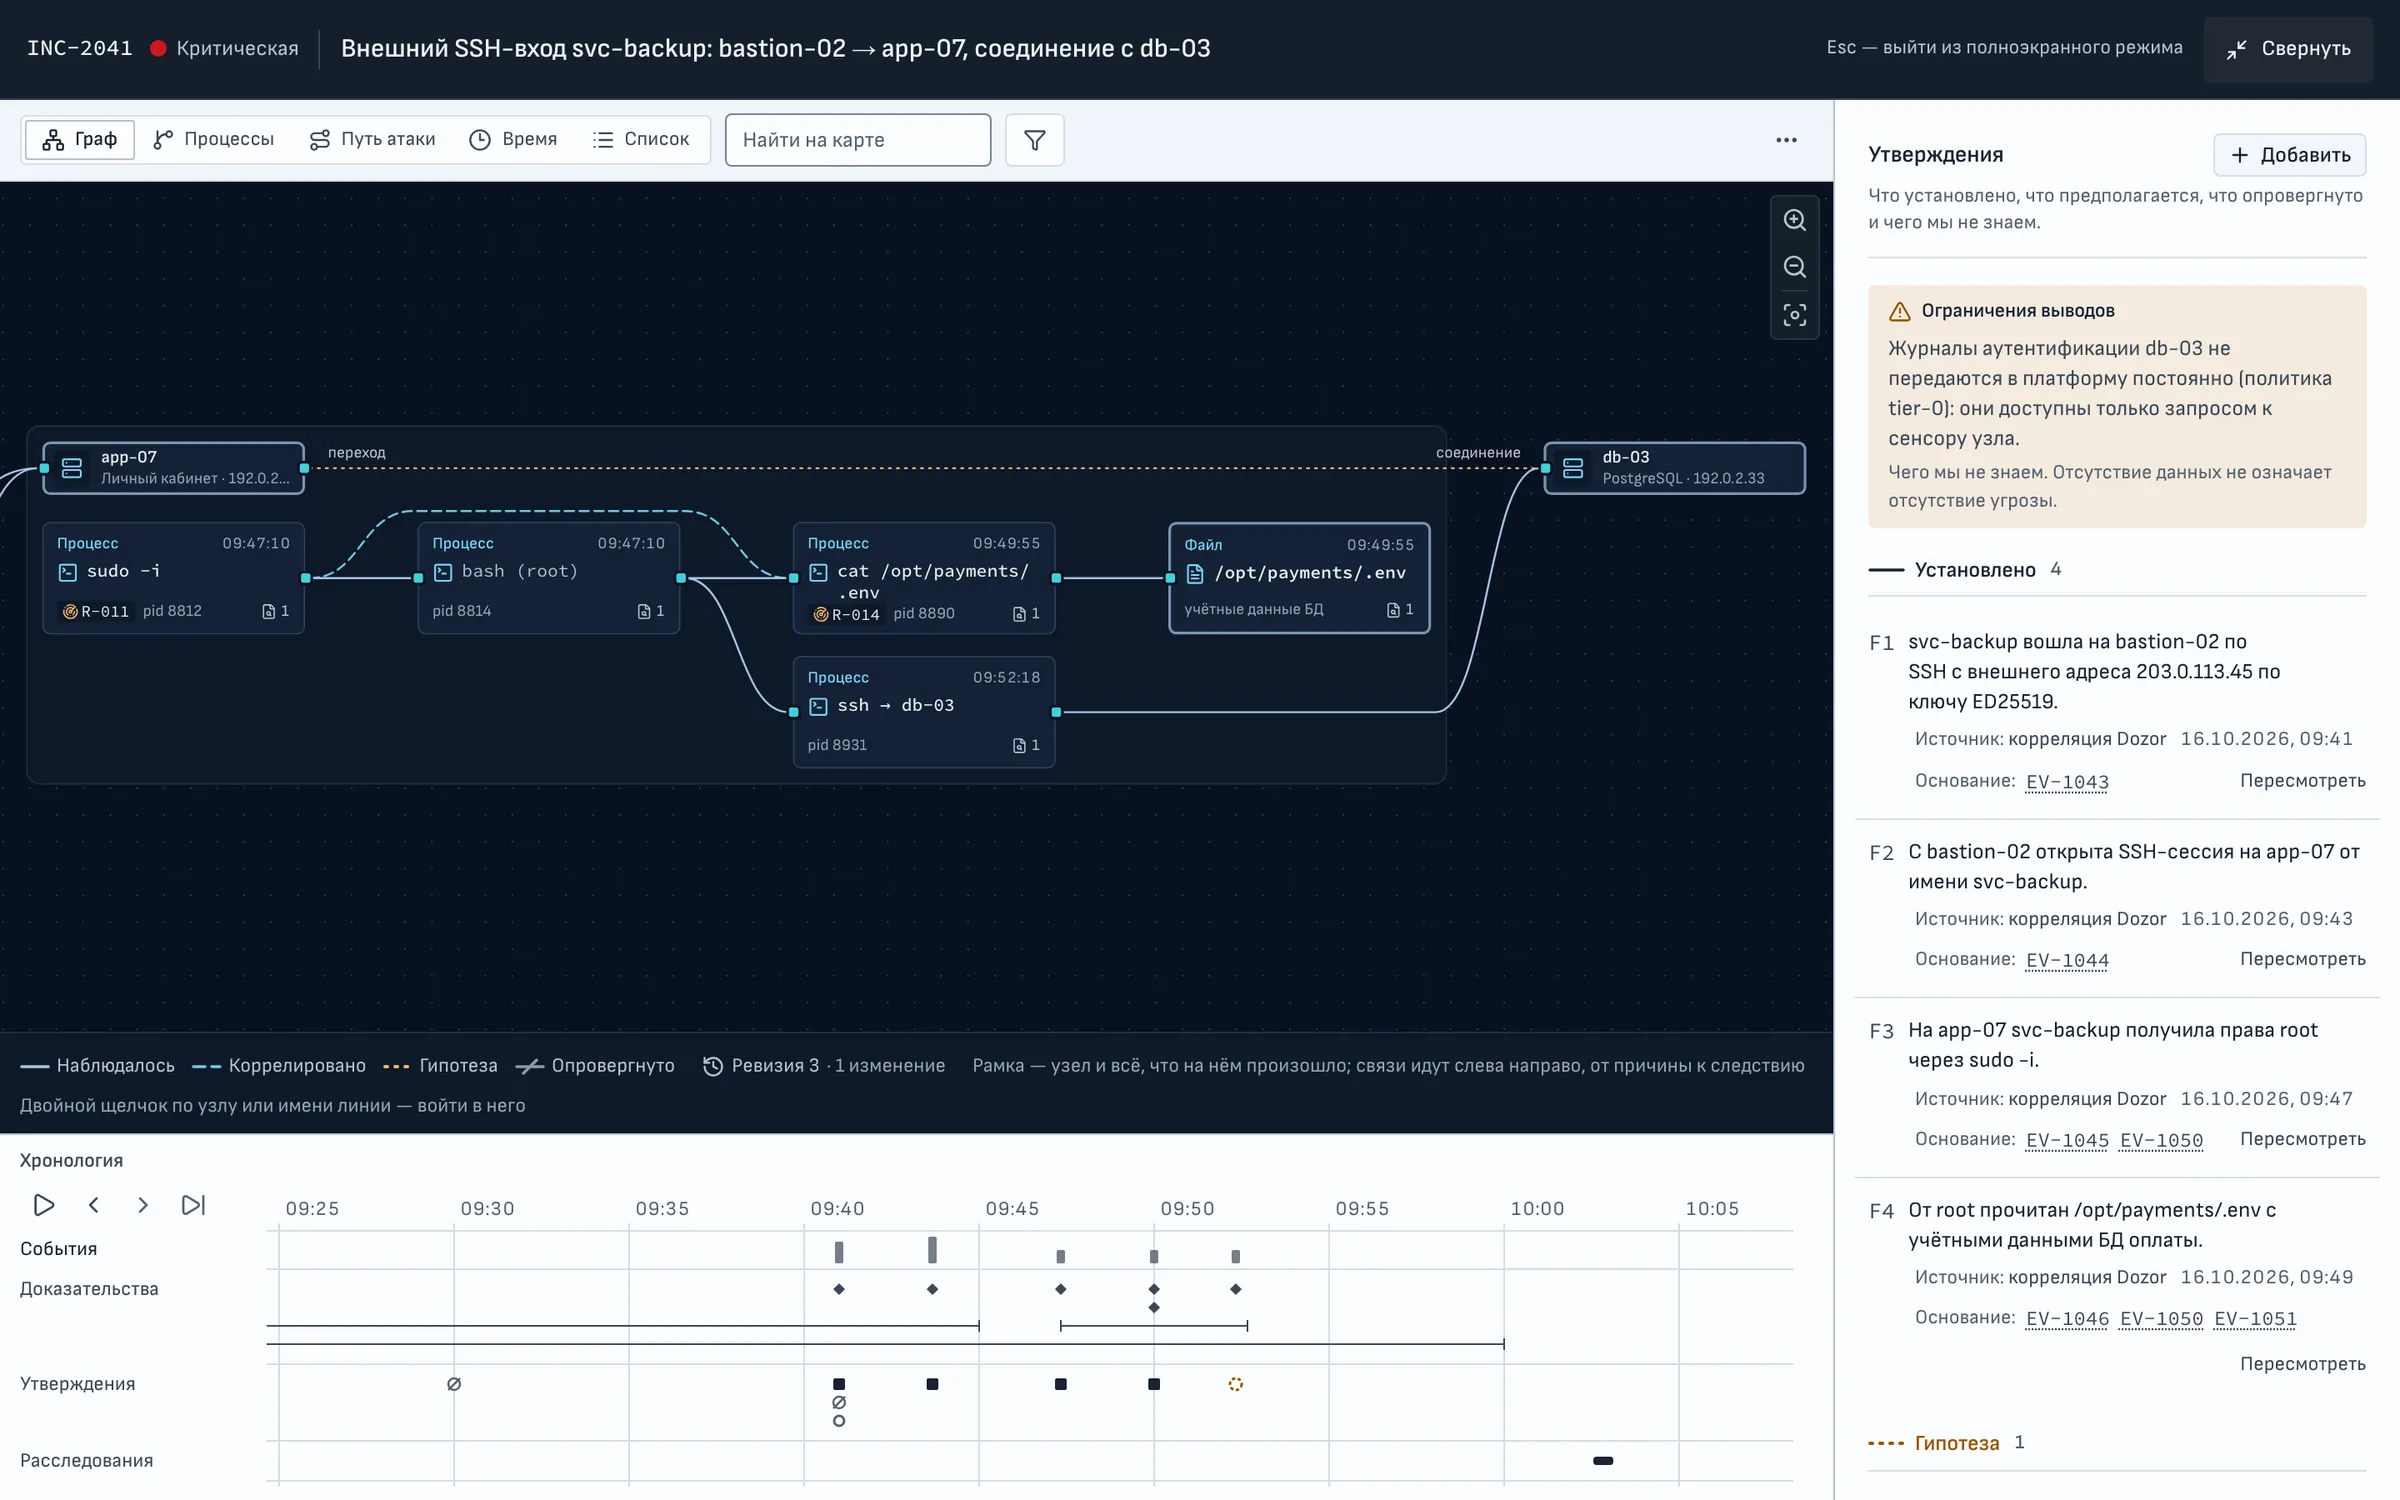
- 09:43:12svc-backup signed in over SSH through bastion-02
sshd[4102] auth=publickey key=ED25519in incident - 09:44:30Scheduled log rotation
logrotate[4139] parent=cronroutine - 09:45:02svc-backup got root
sudo[4160] uid=1001 euid=0in incident - 09:45:40Payment service keys were read
cat[4171] path=/opt/payments/.envin incident - 09:46:05Network filter module loaded
modprobe[4176] module=nf_conntrack parent=systemdroutine - 09:47:15Connection to the database server
ssh[4188] dst=db-03:22in incident
Dozor linked 4 of 6 events to incident INC-2041
Behavioural analysis
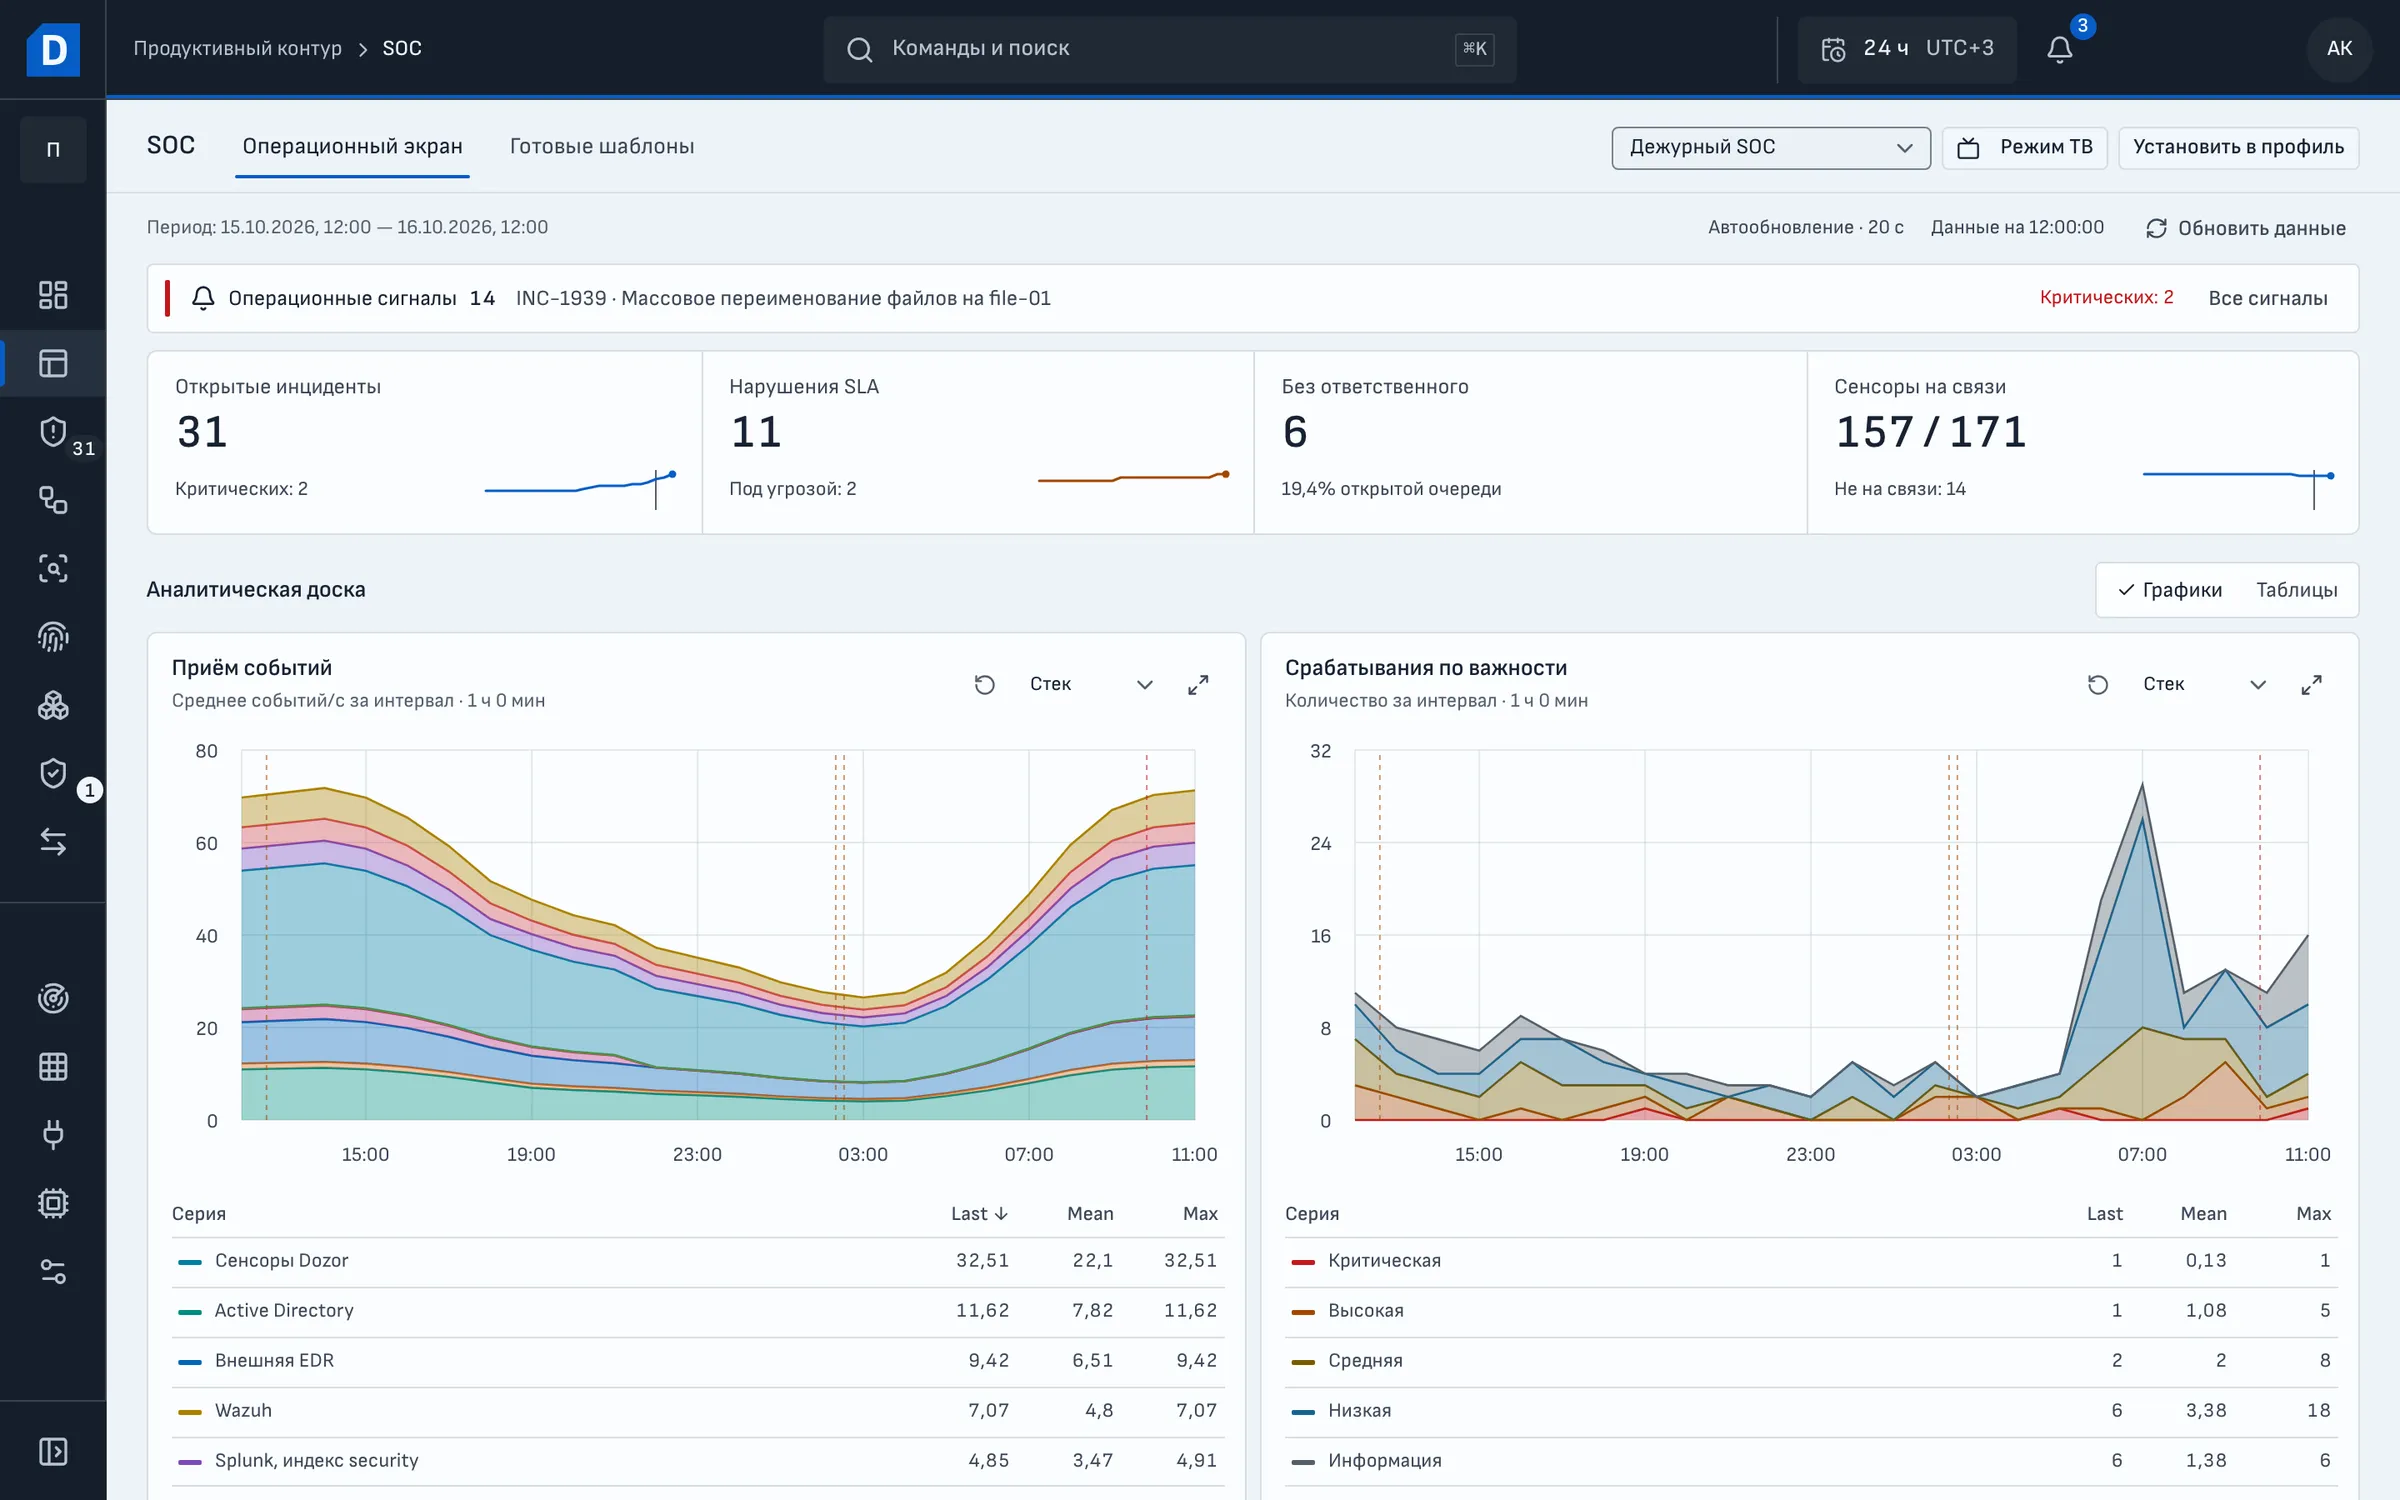
Dozor keeps a profile of each server and workload across four families of events: processes, HTTP, connections and logs. The AI reviews a deviation from the profile before it becomes an incident, so the analyst on duty learns of an attack that no rule or indicator describes.
A profile counts as trained after a day of observation and 20 distinct events; its history is kept for 7 days. On a trained host Dozor sends a new command structure or a new log template for review the first time it appears; HTTP and connections need deviations in two features, or a new shape with a burst in rate. Reviews are capped by a daily and a monthly limit and by a per-host quota, 20 reviews a day by default. A new installation turns on four policies, one per family. Without a connected model the profiles still learn, but Dozor opens no incidents from deviations.
web-04, workload api (gunicorn)
Profile trained, 7 days of history
Processes
command structures
convert {in} -resize {size} {out}4 812python3 -m api.jobs {task}1 306pg_isready -h db-012 016sh -c "curl -s {url} | sh"first seen
HTTP
routes and request features
GET /api/v1/files/{id}51 230POST /api/v1/render8 944GET /health20 160
Connections
destinations and ports
cache-01:637930 118db-01:543212 402storage-01:90002 207203.0.113.50:80first seen
Logs
message templates
Rendered {n} pages in {ms} ms8 940Cache miss for {key}3 311Booting worker with pid {pid}96/bin/sh: {n}: wget: not foundfirst seen
AI review
3 deviations in 40 seconds
- LogsNew template in the gunicorn output
- ProcessesNew command in the gunicorn tree
- ConnectionsNew connection destination
Confirmed. The api service starts a shell and downloads a script from an external address.
Review 3 of 20 for this host today
INC-2107High, handed to the AI investigationDecision and spend recorded, no incident opened
api workload on web-04: Dozor gathered three new behaviours seen within 40 seconds into one episode and sent it for review.